01 · Monitor posture continuously
Kubernetes Security Posture Management continuously reviews cluster configuration against the CIS Kubernetes Benchmark and NSA hardening guidance and controls.
Cloud & Application
Continuous posture, vulnerability, and runtime protection across Kubernetes clusters and cloud-native workloads.
The challenge
Approach
01 · Monitor posture continuously
Kubernetes Security Posture Management continuously reviews cluster configuration against the CIS Kubernetes Benchmark and NSA hardening guidance and controls.
02 · Scan and detect at runtime
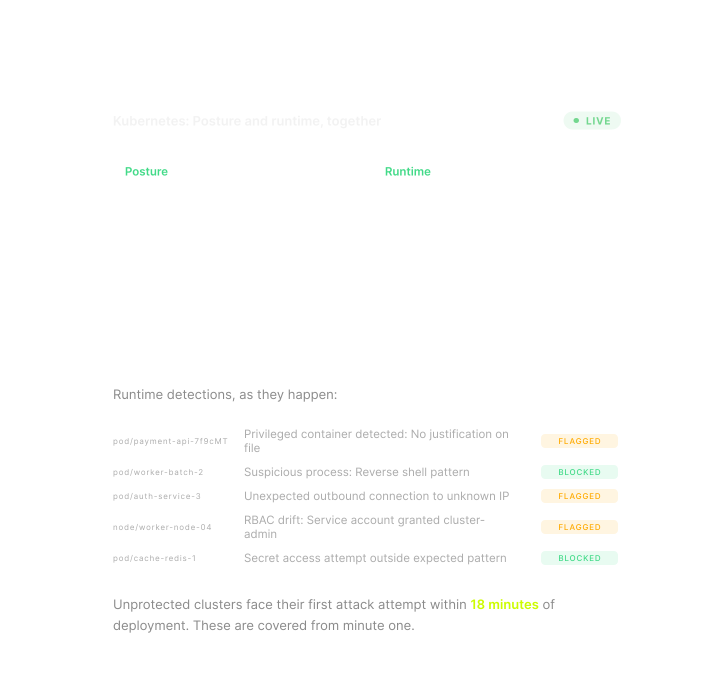
Container images are scanned for vulnerabilities, while runtime threat detection watches for malware, suspicious processes, privileged container abuse, and unexpected runtime behavior patterns.
03 · Review and remediate
You receive a monthly operational review with remediation recommendations for every finding, including prioritized actions, ownership, timelines, risk ratings, validation guidance, executive summaries, progress tracking, and status updates.
How it works
What’s included
Outcomes
Why Gruve
A clean configuration scan does not mean a cluster is safe once it is running. This service pairs continuous posture management with runtime threat detection, so privileged containers, exposed secrets, and suspicious processes are caught while they are happening, not just flagged as a configuration risk after the fact.
Configuration Scanning Alone
Organizations running periodic configuration scans only
Posture management and runtime detection operated end-to-end
Internal team runs scans and reviews results manually
Runtime threats detected as they happen
Risks visible only at the next scheduled scan
RBAC, admission control and workload policy all assessed
Configuration checks only, runtime behavior unaddressed
Privileged container and exposed secret detection included
Manual review required to catch privilege or secret exposure
Cloud & Application
Continuous, unified protection across cloud posture, workload, identity and container risk.
Learn moreReview of Kubernetes cluster architecture, RBAC, container images and secrets management.
Learn moreArchitecture assessment and secure landing zone design for cloud environments.
Learn moreTestimonials
The partnership with Gruve brings significant value to customers by combining thought leadership, delivery, and execution of services. Leveraging AI/ML and Cloud tools in delivering software integrations and services can significantly ease transitions for large enterprise organizations.
Book your assessment
Runtime is where real attacks happen. Make sure someone's watching. Start managed runtime security.
A Gruve advisory lead will reach out within 1 business day.