 Check all thoughts

Sayali Divate:
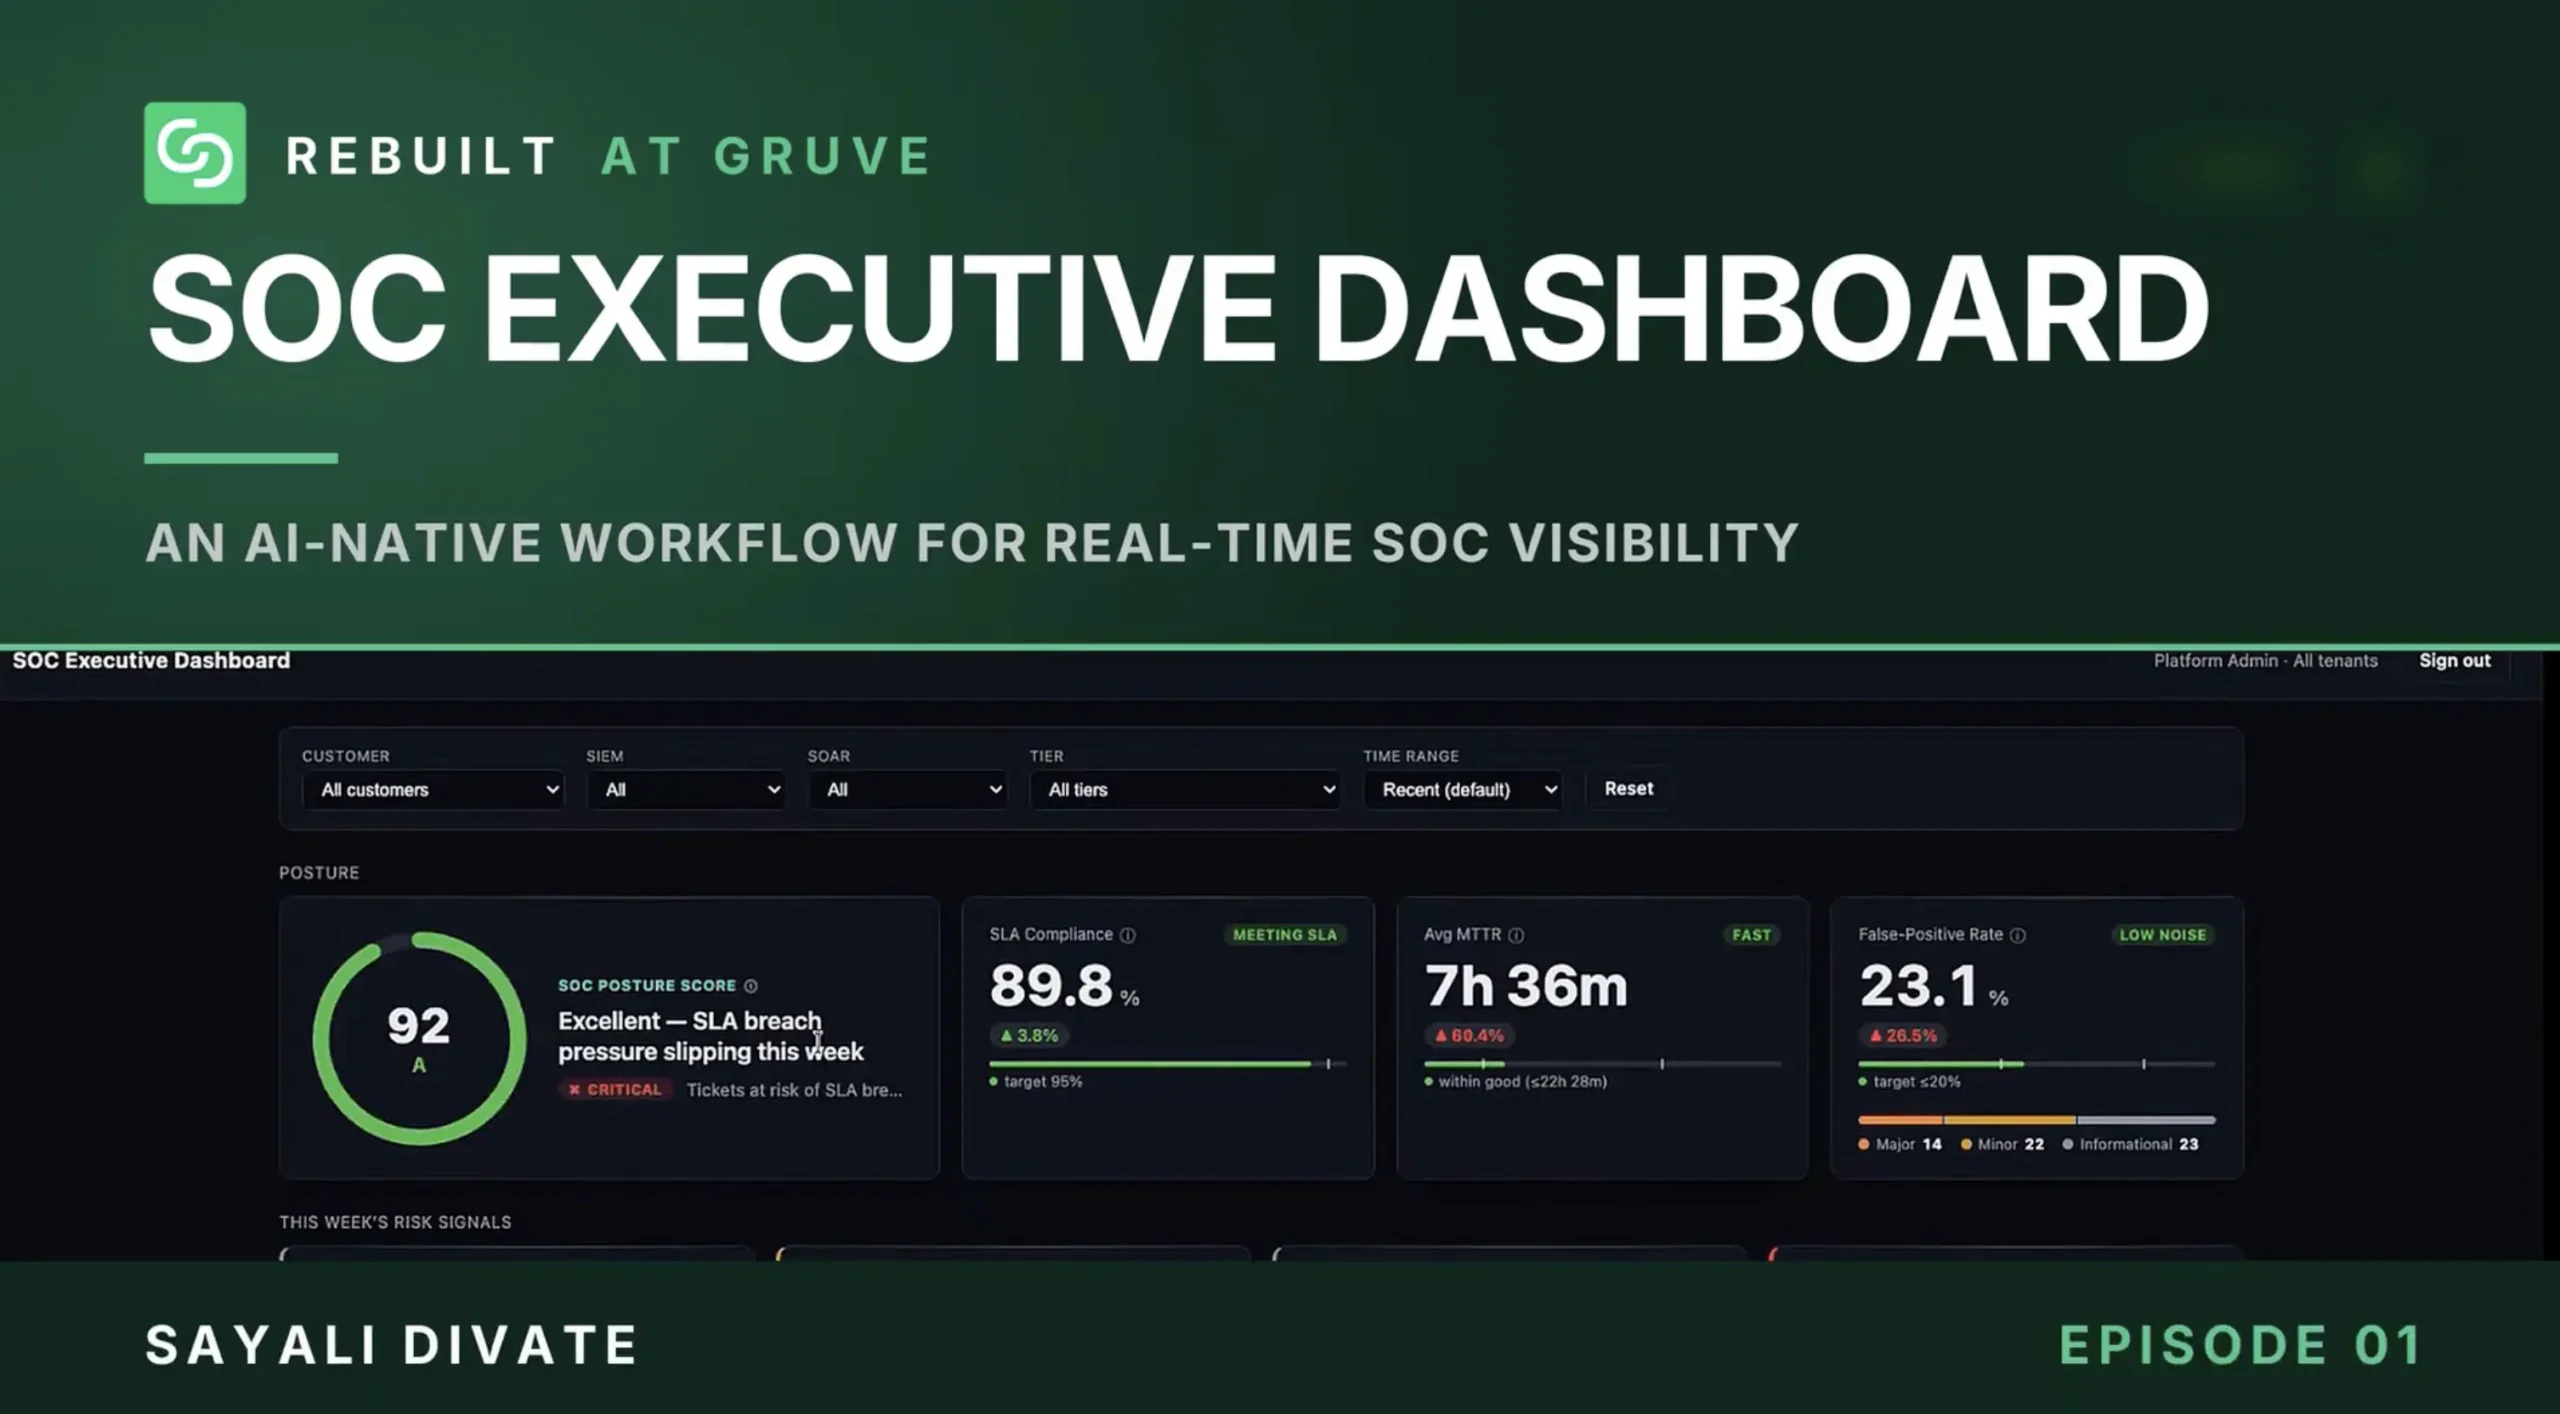
We ran SOC reporting for every customer out of separate reports, assembled by hand. A leader could not look at one screen and tell whether we were keeping up.
So I built the screen. One live view, multi-tenant, scoped server side by JWT so an admin sees the whole portfolio and a customer sees only themselves. Posture score, SLA compliance, average MTTR, false-positive rate. Then the part that gets acted on: this week’s risk signals, and a customer risk ranking sorted worst posture first with the weakest metric named for each one.
Nothing is typed in. Every number is computed off the incident data, so when 19 tickets are sitting at or past their SLA window, that surfaces without anyone building a slide. Reporting that took hours now updates live. Built during our engineering AI hackathon.


